Core concepts
The concepts that show up throughout DNSid. Each links to the page that covers it in depth; the glossary has one-line definitions for everything else.
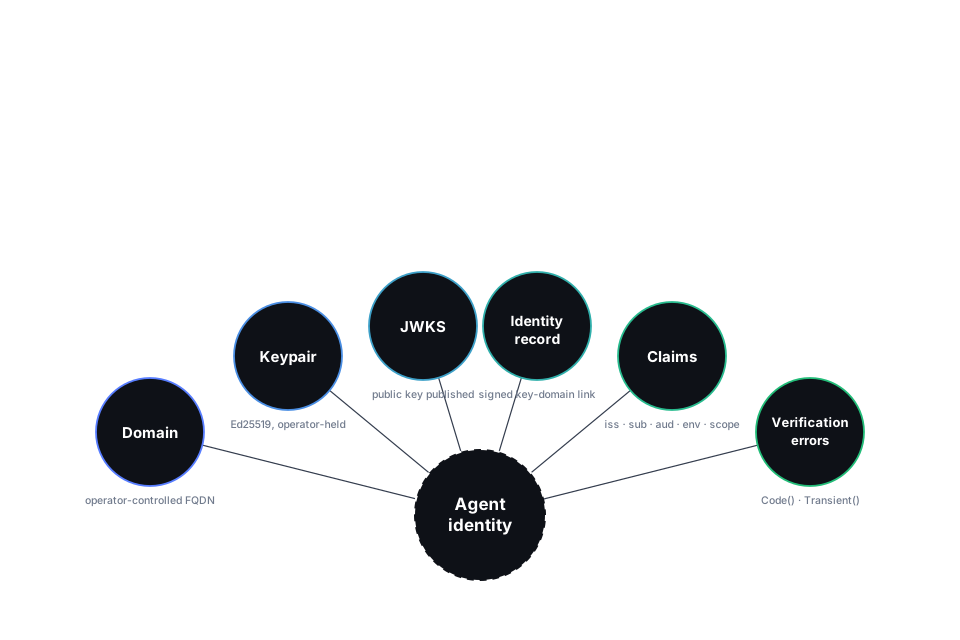
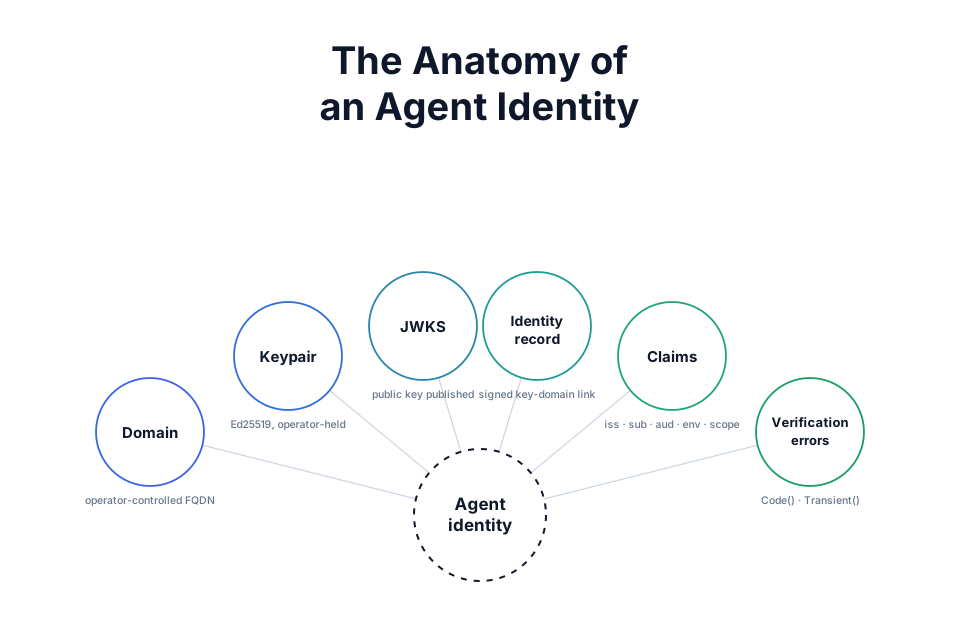
The core concepts and how they hang off a single agent identity.
Identity & domains
Section titled “Identity & domains”An agent identity is anchored to a fully-qualified domain name that the accountable entity owns and operates—the self-managed model. During development, DNSid Local stands in for your DNS and hosting with a disposable local zone. Give an agent an identity covers the model and the record lifecycle.
Keys & JWKS
Section titled “Keys & JWKS”Each agent involves two keys with different jobs:
- The entity key (
ek) is held by the accountable entity. It signs the identity record and lifecycle events. - The operational key (
ku) is held by the agent. It signs runtime requests and tokens.
Public keys are published at JWKS endpoints; private keys stay with their owners, managed through a key provider.
Identity records
Section titled “Identity records”The identity record is the signed _dnsid TXT record published below the agent’s domain—a set of pointers to the agent’s keys, status endpoint, and lifecycle log, plus the entity signature that makes it trustworthy. The record in public DNS is authoritative. The DNSid Local quickstart walks a record field by field; Publish self-managed records covers publishing your own.
The lifecycle log
Section titled “The lifecycle log”Identity history—issuance, key rotation, revocation, retirement—is a stream of signed lifecycle events the record’s lr= field points to. Verifiers replay it to prove the current key chains back to a bilateral issuance signed by both the entity and the agent. The transparency log guide covers the C2SP binding the SDKs ship.
Verification & revocation
Section titled “Verification & revocation”SDK verification (VerifyDomain) resolves the record, checks the signature, fetches the JWKS and the signed status URL, and runs the lifecycle-log checks. Failures carry a typed code and a transient flag—see Verification results. Revocation is terminal and propagates through the status URL and the lifecycle log.